


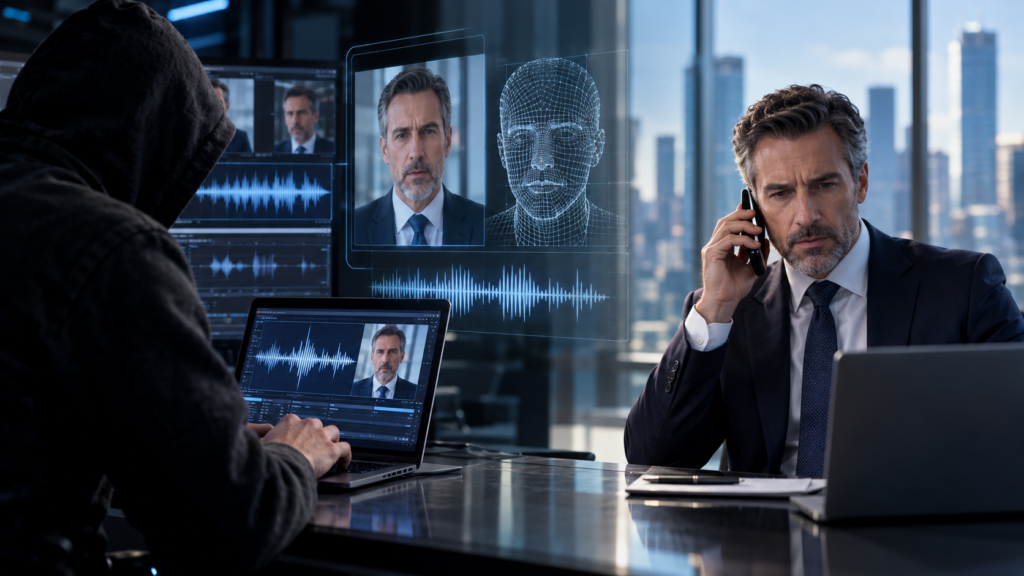
The art of manipulating individuals to obtain confidential information, gain access to protected systems, or initiate fraudulent financial transactions has always relied on human trust as its primary attack vector. What has changed dramatically in recent years is the scale, sophistication, and speed at which these attacks can be carried out, thanks to generative artificial intelligence technologies.
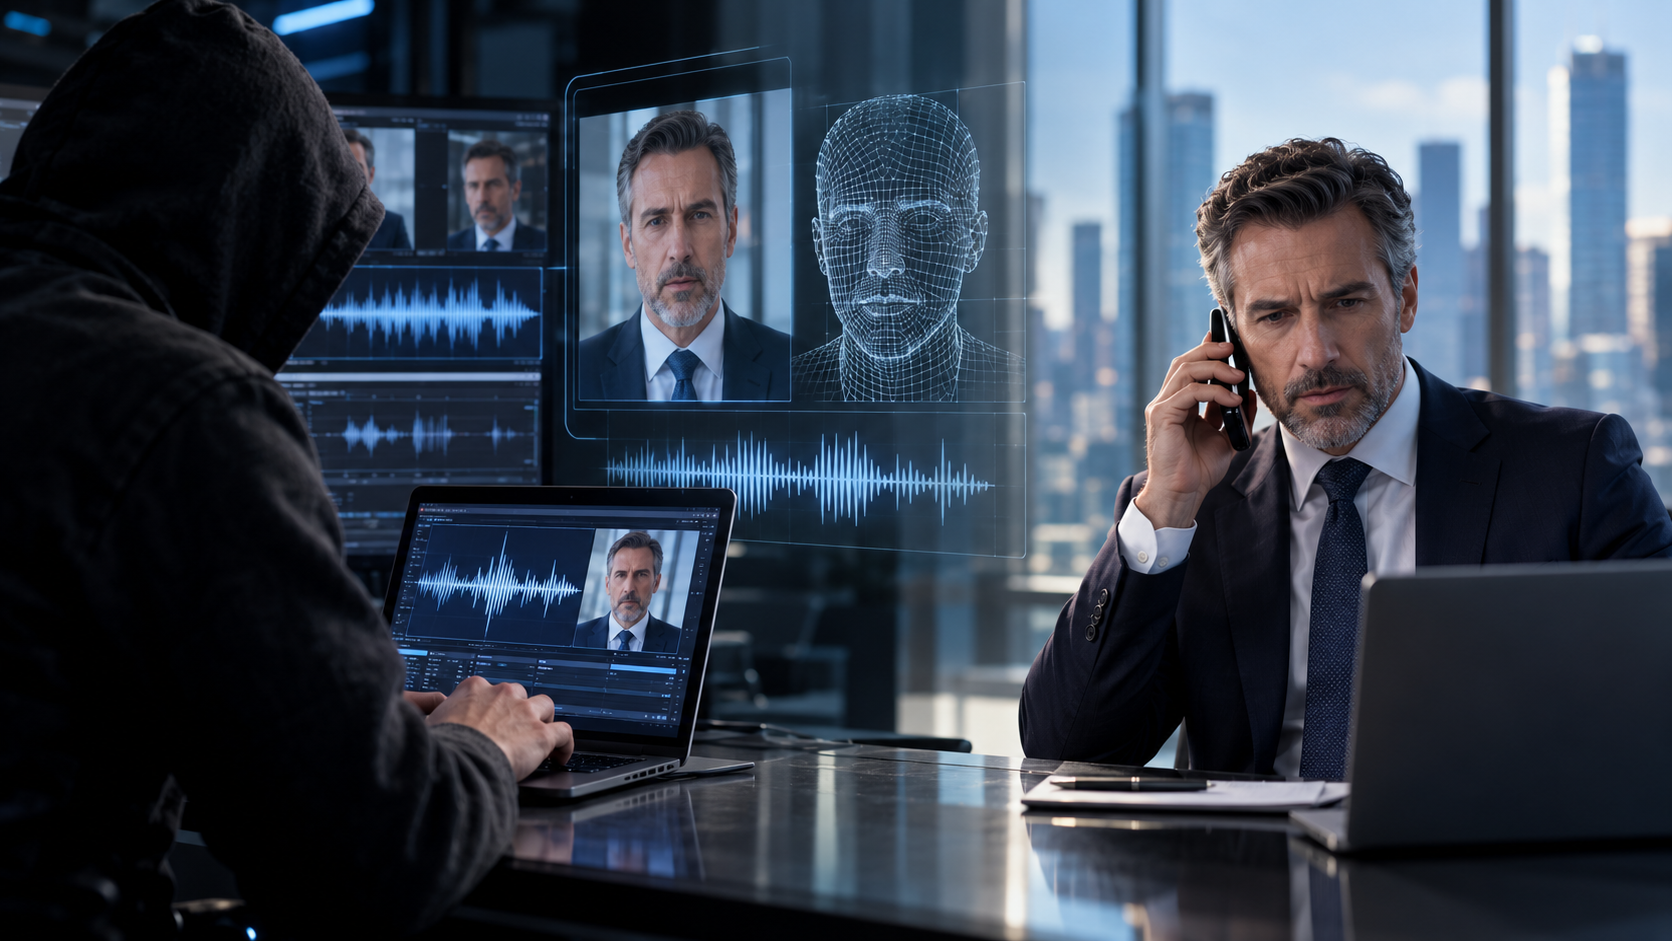
Deepfake video and voice cloning technologies have reached a level of maturity that makes it possible to create highly convincing digital impersonations of corporate executives. Today, an attacker can clone a CEO’s voice using just a few minutes of publicly available recordings, such as a conference presentation uploaded to YouTube, and use it to contact employees, business partners, or financial institutions with fraudulent requests designed to circumvent standard verification procedures.
Real-World Cases and Emerging Attack Patterns
Recent documented incidents illustrate the scale of this threat. In one particularly significant case, criminals used an instant messaging account featuring the profile picture of a major multinational company’s CEO, combined with an AI-generated voice clone created from publicly available video footage, in an attempt to defraud a business partner. Although the attack was unsuccessful, it demonstrated both the technical feasibility and the potential severity of this emerging threat.
These are not isolated incidents. Voice deepfake fraud targeting corporate finance teams is becoming an increasingly serious concern. Criminals identify internal reporting structures by analysing publicly available organisational charts and professional social media profiles. They then select the most favourable moment to strike, often while the impersonated executive is travelling, when direct verification may be more difficult, and contact employees with urgent requests to transfer funds or disclose sensitive information.
Why Traditional Defences Are No Longer Enough
Defences based exclusively on technical controls, such as anti-phishing filters and authentication systems, are insufficient against attacks that exploit interpersonal trust rather than technological vulnerabilities. An employee receiving an urgent phone call that appears to come from their CEO may not instinctively activate cybersecurity protocols. Instead, they are likely to respond according to established hierarchical expectations and organisational norms.
The effectiveness of AI-powered social engineering lies precisely in its ability to exploit legitimate organisational behaviours. A culture of urgency, respect for authority, and willingness to cooperate are qualities that organisations actively encourage, yet attackers can turn these same qualities into vulnerabilities.
Prevention and Resilience Strategies
Effective protection against advanced social engineering requires an integrated approach combining human awareness, organisational procedures, and proactive intelligence.
At an organisational level, implementing multichannel verification protocols for all critical communications is essential. Any request involving financial transfers, credential disclosure, or changes to operational procedures should be independently verified through a trusted communication channel different from the one used to initiate the request.
Employee training must evolve beyond traditional, generic security awareness programmes towards realistic simulations that reproduce attack scenarios involving deepfakes and voice cloning.
Employees should be trained to recognise warning signs, including unjustified urgency, unusual requests, and pressure to bypass established procedures, and to follow verified response protocols even when the person making the request appears to be a senior executive.
The Role of OSINT in Prevention
Open-Source Intelligence (OSINT) plays a crucial role in preventing advanced social engineering attacks.
Assessing executives’ digital exposure — including what publicly available information could be used to create a convincing deepfake, which voice recordings are accessible online, and what professional or personal relationships can be reconstructed through social media — allows organisations to anticipate potential attack vectors and proactively reduce their exposure to risk.
Continuous monitoring of open sources can also help identify early indicators of an attack in preparation, such as attempts to gather specific information about an executive through preliminary social engineering, the creation of fake profiles impersonating corporate leaders, or the registration of lookalike domains designed to support targeted phishing campaigns.
How Kriptia Can Help
Kriptia provides organisations with an integrated approach to preventing and defending against advanced social engineering threats, combining OSINT expertise, specialised training, and security management.
Kriptia’s services include the design of tailored verification protocols for critical communications, the development and execution of realistic attack simulations involving deepfake and voice cloning scenarios, and continuous open-source monitoring to identify potential targeting activities during their preparatory stages.
Kriptia also supports organisations in developing corporate policies that balance executives’ need for public visibility and communication with the protection of their digital identities.
By combining proactive intelligence, organisational resilience, and targeted training, Kriptia helps organisations strengthen their defences against a threat landscape in which seeing and hearing can no longer be considered sufficient proof of identity.